Despite Trezor’s claims today that none of its devices were compromised – unlike rival Ledger’s devices – hacker Joe Grand claims to have found implants in two Trezor devices and reported it to the company in August.
I published an article this morning about implants discovered in a number of Ledger crypto devices. Initially, he included in the story information about implants that had also been discovered in devices made by Trezor – Ledger’s main competitor. However, I deleted it before publishing the story because I didn’t want to confuse things.
But a few hours ago, Trezor announced on X that it would reduce the number of merchants allowed to sell its devices out of an “abundance of caution.” Chief Commercial Officer Danny Sanders wrote that there was “not a single piece of evidence that Trezor devices were compromised,” and that this was reducing its list of authorized sellers simply as a “preventative measure” to have better control over its supply chain.
To the resellers who helped build Trezor: thank you and I’m sorry 💔 pic.twitter.com/RK7KBJOshp
– Danny (@Dantoshi) October 13, 2026
But that’s not entirely true. Notorious hacker Joe Grand recently found implants in two Trezor wallets and notified the company in August. I did not include this in my Ledger story because the circumstances were different from the Ledger incidents. The Ledger implants became news because they were 1) sold in devices distributed by authorized resellers of Ledger devices and 2) the implants were then used to steal $100 million in crypto from owners of compromised devices.
But as I noted in the Ledger article, Grand initially found implants in four Ledger devices sold online by unauthorized Ledger merchants. These traders appeared to be clandestine sellers who appeared on online marketplaces only to disappear after days or weeks. The provenance of the compromised devices was therefore already uncertain, unlike later implants sold by reputable and authorized sellers.
The Grand implants found in the Trezor One and Trezor Model T devices were Also sold by unauthorized third-party sellers – not reputable authorized sellers. This isn’t really a surprise, since Ledger and Trezor have for years advised customers to buy directly from their own websites or from authorized merchants. Therefore, the news that Grand found Trezor wallets compromised by implants did not seem newsworthy. Especially since three years ago, Kaspersky Lab researchers also discovered an implant in a Trezor wallet sold on a popular Russian market. In its report, Kaspersky called it a fake wallet, but it was a real Trezor wallet that had been compromised.
Given that the first Ledger implants appeared in devices sold by unauthorized sources – only to later also appear in devices sold by authorized sources – and given that Trezor has publicly denied knowing that any of its own devices had been compromised, I think it is now relevant to disclose the information Grand provided to me about the compromised Trezor wallets it found. Especially because it is possible that these findings are a precursor to the appearance of implants in Trezor devices sold by authorized resellers. The fact that Trezor announced that it was withdrawing authorization from some of its resellers shows that it may also be concerned that the implant problem could spread to devices sold by authorized sellers.
If you find this article useful, you can leave a one-time tip to express your gratitude to the author.
Trezor One and Trezor Model T Implants
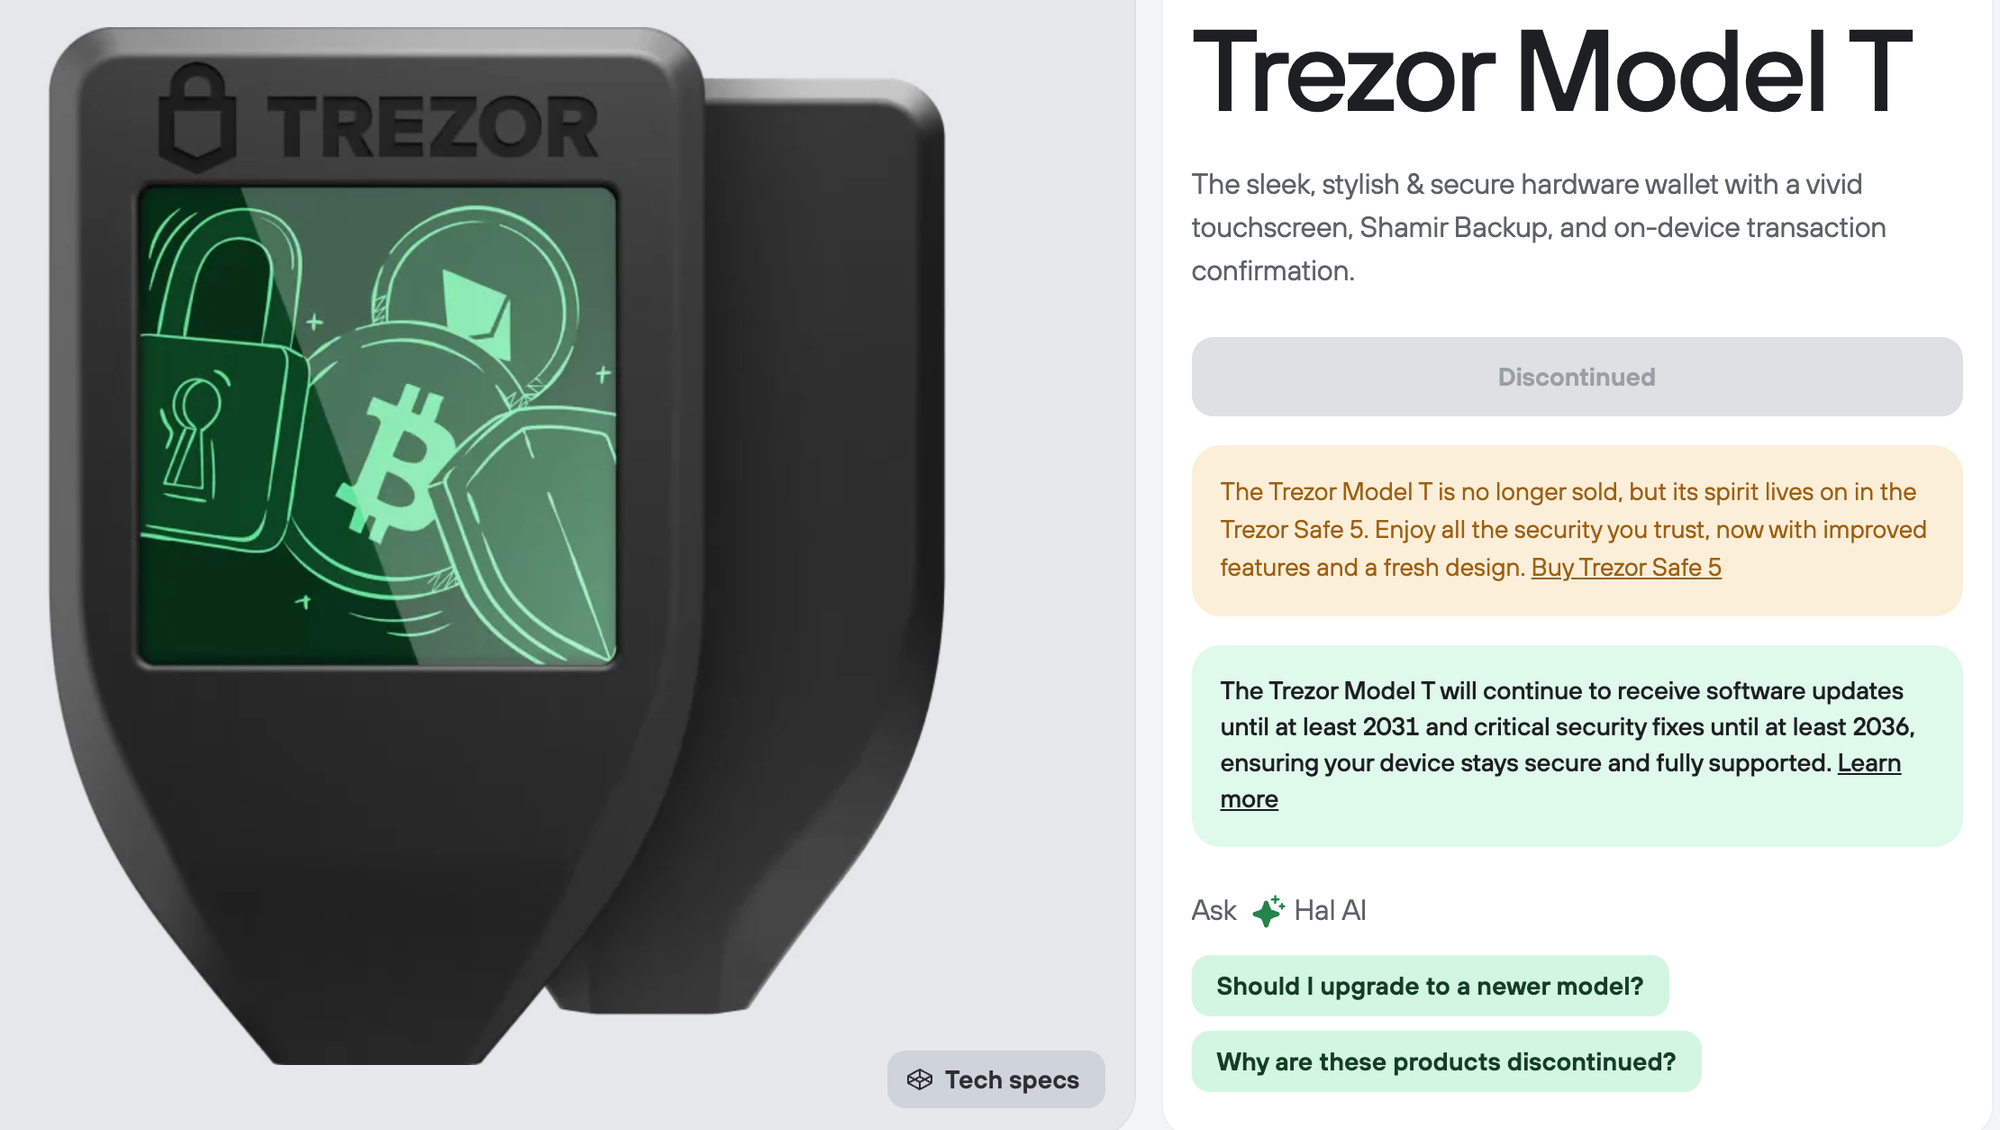
Grand found one implant in a Trezor Model T wallet that someone purchased through Facebook Marketplace in Canada in 2025 and another in a Trezor One device that someone got from a TikTok store in August. The Trezor One buyer became suspicious when around $50 was transferred from his crypto account. The Trezor One and Trezor Model T are discontinued devices, but Trezor still supports them (as shown in the product photo at the top, the company will continue to distribute software updates until 2031 and security updates until 2036) and customers still purchase them from third-party sellers.
In both wallets, the attackers had replaced the microcontroller on the devices so that instead of generating random recovery seed phrases, the controllers generated one of dozens of predetermined seed phrases that the attackers had coded into the controllers, allowing them to guess the crypto accounts’ recovery seeds.
Grand claims that legitimate microcontrollers used in Trezor devices have code protection features intended to prevent anyone from accessing and modifying the code. But because the Trezor code is open source, it was easy for attackers to obtain the code, modify it, and program it into a new, insecure device by simply replacing the legitimate chip with their own chip.
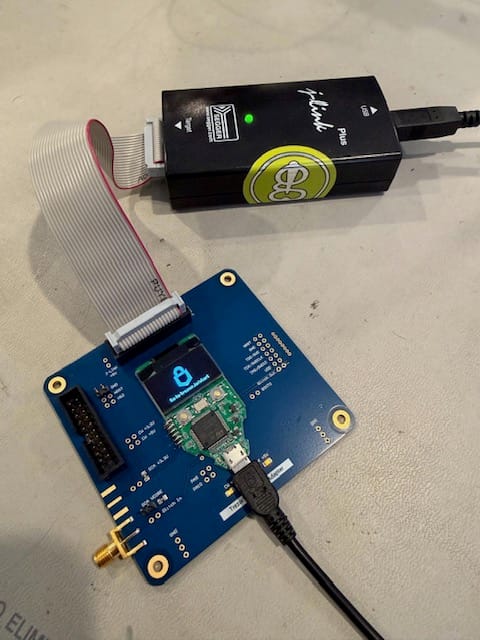
Grand says he wrote to Trezor about the Model T implant on August 10 of this year and received a very cordial response three days later:
Thank you for reaching out and sharing such detailed technical results. This is very interesting and we appreciate the work you put into investigating the device.
Based on your description, the device has very similar characteristics to counterfeit or modified Model T devices discovered in Russian markets in 2022-2023. A particularly interesting twist on these earlier devices is the use of a replaced MCU and modified firmware, along with an external microSD card containing legitimate firmware for integrity checking.
We would definitely be interested in looking at the binary you extracted from the STM32F427. If you can share it with us, please send it to us.
We would also be very interested to know how the latest version of Trezor Suite behaves when this device is connected. Does Trezor Suite recognize or flag the device as counterfeit or indicate something is wrong?
Although we have discontinued sales of the Model T, we continue to improve Trezor Suite’s controls to identify counterfeit and modified devices. So any information you can provide on how the current version of Trezor Suite handles this particular unit would be very helpful.
Thank you again for bringing this to our attention and sharing the technical details of your investigation.
We would be interested in hearing about any additional findings as your reverse engineering continues.
Notably, in its latest communication from Trezor in early September, the company copied its PR manager into the email and told Grand: “If you are considering publishing something, we would appreciate being informed so that we can review it and, if appropriate, also provide public comment in advance.”
Naturally, Grand was surprised today to see Trezor publicly stating that it was unaware of any of its compromised devices.
Trezor implants differ from Ledger implants in several ways. Ledger implants simply sit quietly on the wallet until the device owner initializes it for the first time, which causes the device to randomly generate a recovery seed phrase. The implant then records the seed phrase as it is sent to the device screen for display to the user, and stores it for later use. At some point, the implant connects to a nearby cell tower and transmits the stored seed data to the attackers.
Trezor implants work differently in that attackers installed malicious firmware on the device containing pre-generated seed phrases that the attackers know. The malicious firmware then “generates” one of several pre-generated seed phrases and displays it to the user – who thinks the seed was randomly generated by their device.
Ledger implants do not affect the functionality of the device and therefore cannot be detected by Ledger integrity checks. But because Trezor implants operate their own version of compromised code, they must therefore be able to bypass the software integrity checks that Trezor devices are subject to. They do this by first performing integrity checks on a copy of legitimate firmware, before allowing malicious behavior to take over.
I’ve reached out to Trezor for comment and will update this story if they respond.
See also:
Who installs backdoors in Ledger crypto wallets?
Gn bussni