Malicious actors now rely on agent workflows powered by AI-driven offensive frameworks to automate the discovery and exploitation of vulnerabilities, accelerating attacks to machine speed.
Although AI was initially used experimentally in the attack stream, the Google Threat Intelligence Group (GTIG) has observed its widespread adoption by both financially motivated and state-sponsored threat groups.
A notable example is the use of CAIRN, an open source multi-agent penetration testing framework, in an attack on the US aerospace sector, and suspected North Korean hackers using Claude Code to distribute malware.
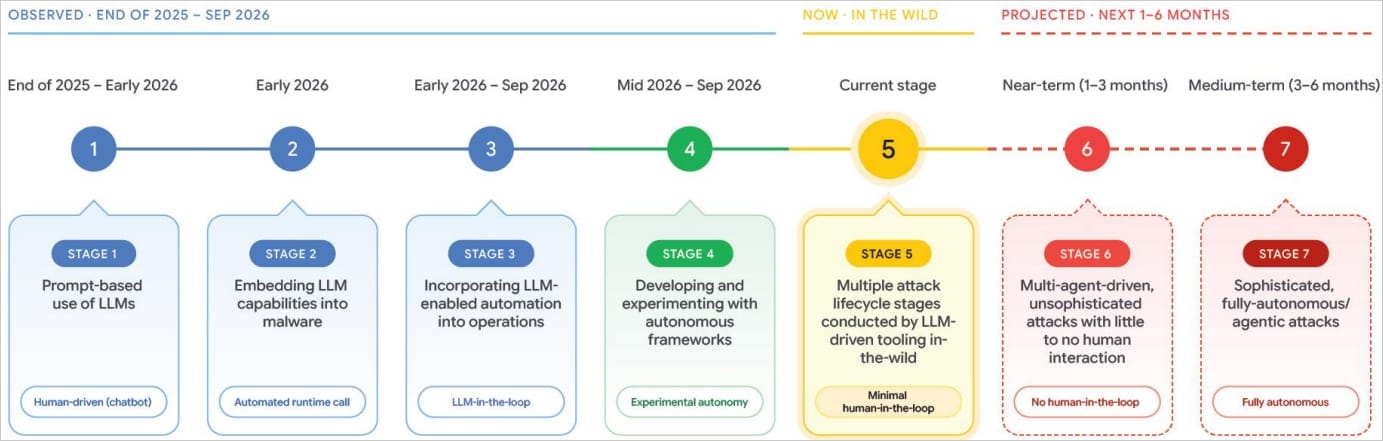
The researchers estimate that over the next three months, malicious actors will be able to launch simple attacks that require “little or no human interaction” and primarily rely on multiple AI agents.
Their projection is that “sophisticated and fully autonomous” agent attacks are likely to emerge over the next six months.
Evolution of the use of AI in cyberattacks Source: Google
In an advisory issued last week, the FBI warned that several malicious actors began using the ARTEX AI penetration testing framework since August and launched attacks against organizations in finance, government, technology, defense, healthcare and other industries.
Using AI to find and exploit vulnerabilities
Google says attackers are now systematically abusing open source penetration testing suites to launch fully automated attacks, including ARTEX, CAIRN, CyberStrikeAI and HexStrike AI.
Attackers used these frameworks to carry out adaptive attacks against endpoints exposed to the Internet and vulnerable to low-complexity vulnerabilities for which large language models (LLMs) could easily create exploits.
In one example highlighted by GTIG in its AI Threat Tracker report, hackers used a multi-agent system called “exploit_agent” to fully automate the search and exploitation of vulnerabilities in attacks targeting French media, entertainment and education websites.
“In the last quarter, GTIG identified for the first time malicious actors using LLM frameworks to fully automate the discovery and exploitation of vulnerabilities without a human being involved,” Google explains.
“Specifically, GTIG identified an exposed middleware server hosting a multi-agent vulnerability scanning and weaponization framework, dubbed exploit_agent, which integrates with multiple border and local LLMs.”
Google discovered this framework from the attacker’s exposed intermediary server, which also included stolen victim data, reconnaissance information, webshells, and brute force scripts.
The system scans software updates of popular web applications for signs of security vulnerabilities and automatically attempts to exploit them.
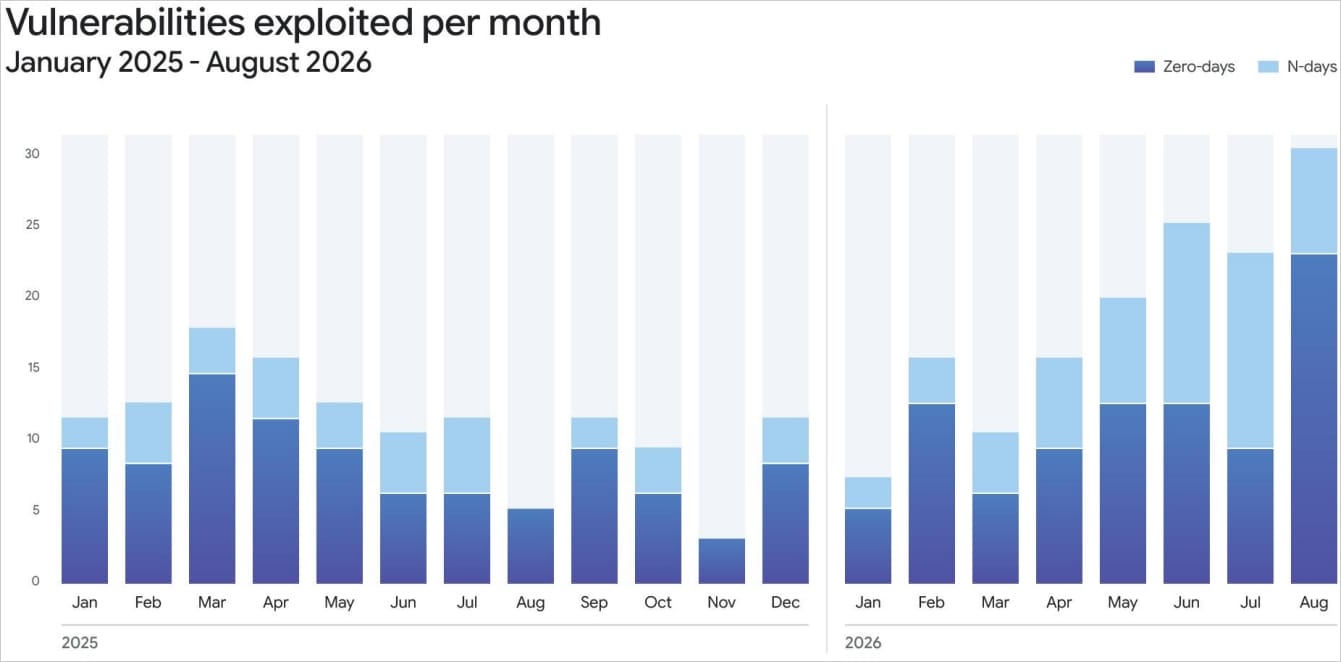
Google warns that deploying such frameworks in attacks has significantly reduced the time defenders have to patch their systems, while also producing false leads.
Researchers noted the recent example of PHP2Shell, where hundreds of proof-of-concept (PoC) exploits, most of them generated by AI, appeared shortly after PHP announced the two flaws. This added a significant burden to defenders, as they had to review the code and develop protections.
Monthly volume of exploited vulnerabilities Source: Google
Other AI usage trends
Beyond automated attacks, Google spotted several attacks originating from UNC6836, a cluster of activity believed to be linked to “Midnight Neptune,” targeting cryptocurrency companies in North America and Europe, using modified Claude code.
After the initial compromise, the attackers modified the settings of the Claude Code application so that upon launch it triggered the download of the SOMBERMEME backdoor.
Google reports that AI is now regularly used in influence operations by state-backed groups, commercial vendors and political networks.
According to the researchers, LLMjacking has become a widespread problem, with attackers increasingly exploiting this new source of revenue at a significant cost to affected organizations.
Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what’s happening with a 14-day read-only scan of Microsoft 365 or Google Workspace, without MX modifications.